


- Main page
- Scameter
- Cyberdefenders Alliance
- FPS Suspicious Proxy Alert
- IT basics
- Secure Your Device
- Parents & Teachers
- Cybercrime
- Resources & Events
- My Account
- Logout

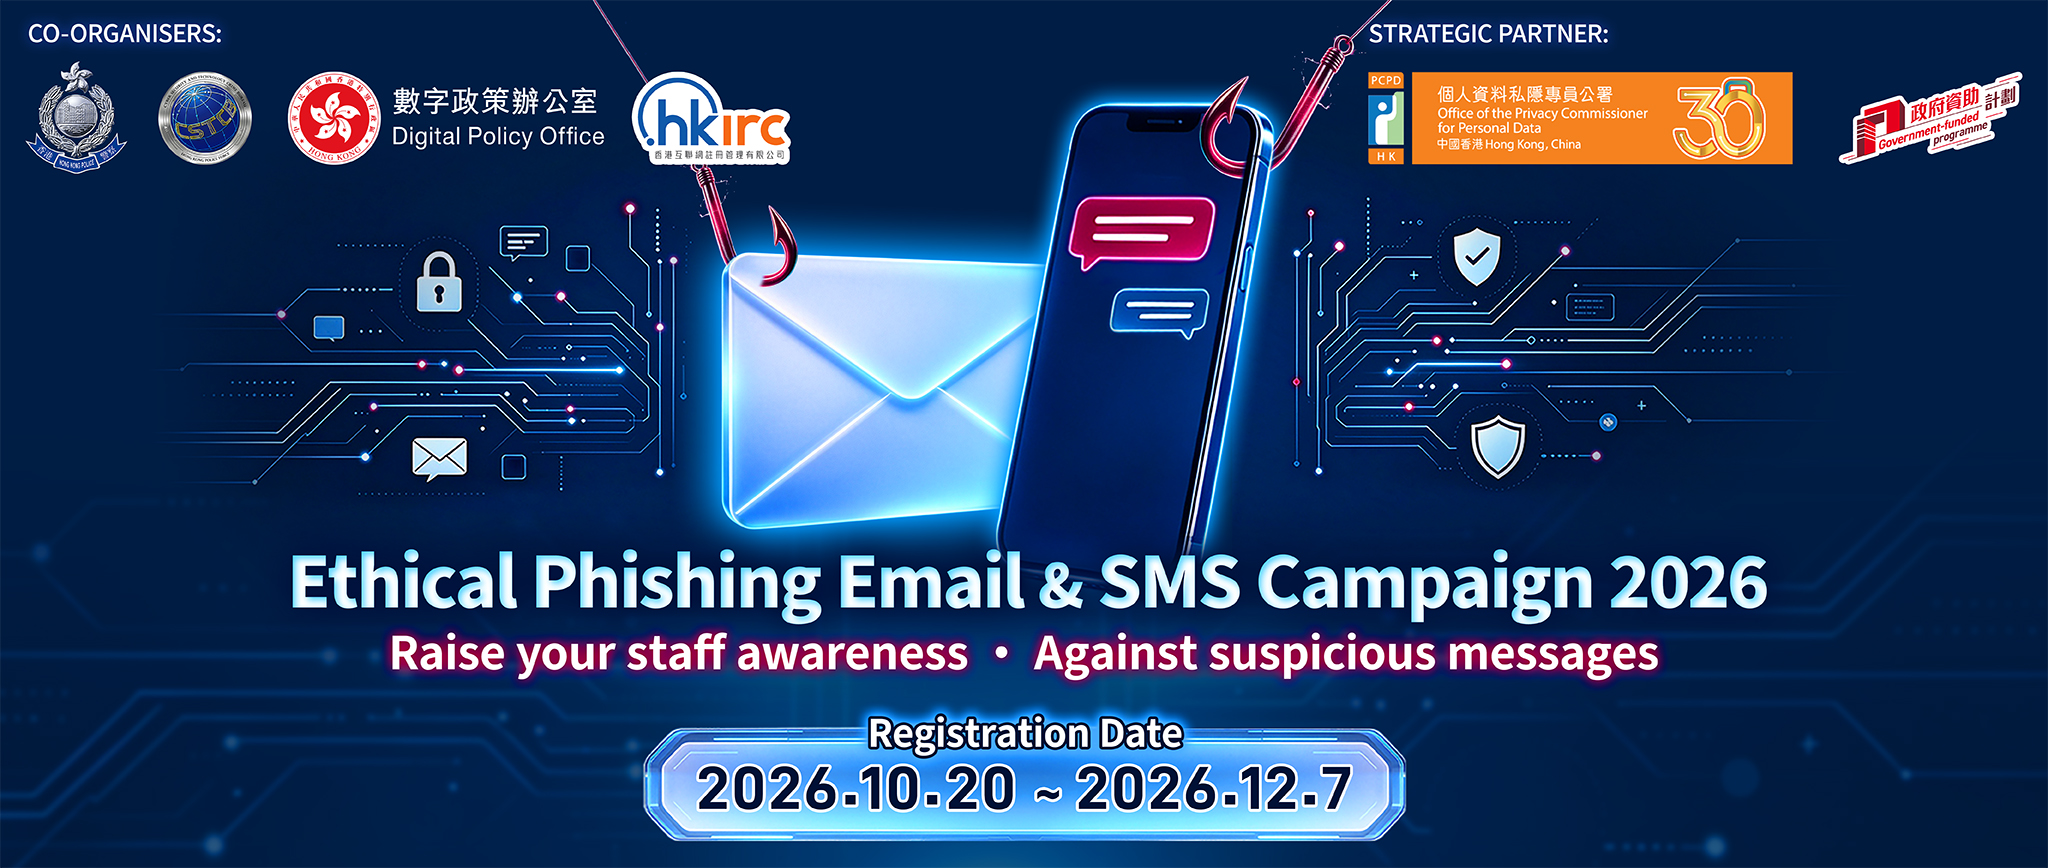
“Ethical Phishing Email and SMS Campaign 2026” Returns — Say “No” to Phishing Traps Together!
Co-organised by the Cyber Security and Technology Crime Bureau (CSTCB) of the Hong Kong Police Force, the Digital Policy Office (DPO), and Hong Kong Internet Registration Corporation Limited (HKIRC), with the Office of the Privacy Commissioner for Personal Data (PCPD) as a strategic partner, the ” Ethical Phishing Email and SMS Campaign 2026″ cordially invites organisations to join hands in building a strong defence against phishing attacks.
A Proven Track Record Widely Recognised by the Industry
Last year’s campaign received widespread industry engagement, achieving encouraging results: the phishing email exercise attracted over 300 organisations and more than 53,000 employees, while the phishing SMS exercise saw participation from 30 organisations and over 3,600 employees. Participating organisations widely agreed that the exercises effectively raised employees’ awareness of identifying suspicious emails and SMS messages, thereby reducing cybersecurity risks for both organisations and their staff.
Keeping Pace with Scam Trends — Enhanced Test Scenarios
Phishing scam messages have become increasingly rampant in recent years, with tactics evolving constantly — from fraudsters impersonating customer service representatives and luring victims to call fake hotlines, to impersonating instant messaging companies to steal account credentials. In response, this year’s phishing SMS campaign will introduce a new test item: phishing SMS messages containing call-back “customer service” phone numbers, to further heighten employees’ vigilance against suspicious messages both at work and in daily life.
Campaign Details
During the campaign period, the organisers will send simulated phishing emails and/or SMS messages at irregular intervals to the email addresses and corporate mobile phone numbers provided by participating organisations, in order to test employees’ cybersecurity awareness. Upon completion of the campaign, each participating organisation will receive a detailed assessment report reflecting employees’ overall performance in handling suspicious emails and/or SMS messages, helping organisations identify security weaknesses and make targeted improvements.
Enrolment
Interested organisations may submit the enrolment form via the link below on or before 7 December 2026:
- • Organisations may choose to participate in either one or both campaigns — free of charge
- • Each organisation may register up to 200 employee email addresses and/or 200 corporate mobile phone numbers
- • Each organisation must designate one contact person to coordinate and follow up on registration matters
- • Quota is limited and allocated on a first-come, first-served basis
If you have any enquiries, please feel free to contact us via email:
or call us at 36617713.
Remarks: Only email addresses registered under the organisation’s domain name are eligible to participate in this exercise. Web-based email addresses such as Gmail are not applicable.
